

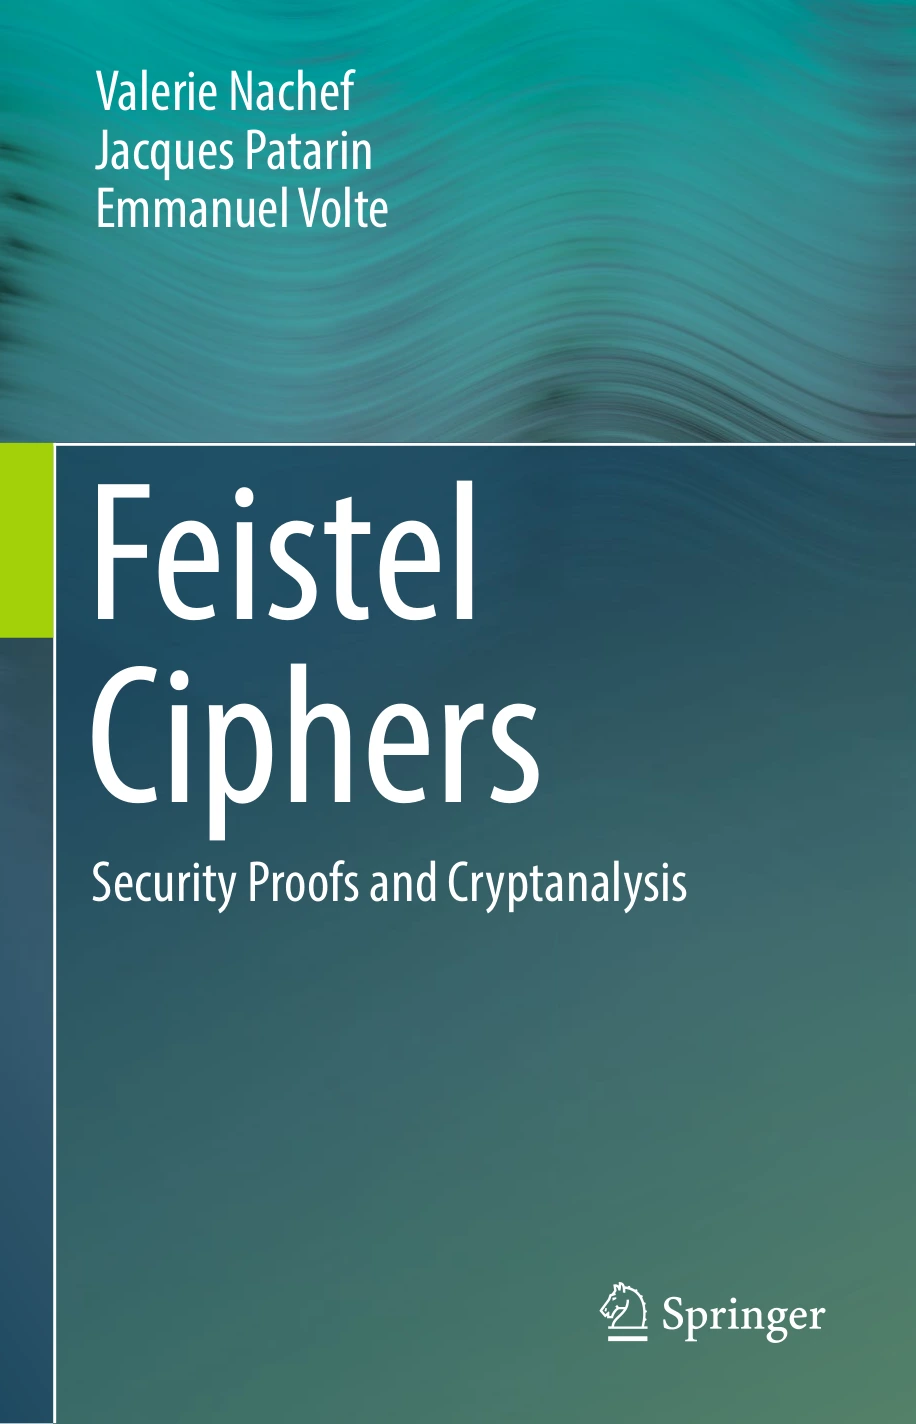
Feistel Ciphers: Security Proofs and Cryptanalysis
Original price was: $123.49.$61.74Current price is: $61.74.

Valerie Nachef
Product Specs:
- File Type: PDF
- File Size: 3.5 MB
- Book Language: English
- Total Page Count: 310
- Instant Download
Feistel networks sit at an important intersection of cryptographic theory and real-world cipher design. This technical survey examines how these constructions behave, how their security can be proved, and how their weaknesses can be tested through generic attacks and cryptanalysis.
Valerie Nachef, Jacques Patarin, and Emmanuel Volte move from foundational definitions to detailed studies of established and generalized Feistel designs. The result is a research-focused account for readers who want to understand not only the construction of these ciphers, but also the reasoning used to evaluate their security.
From Feistel fundamentals to security arguments
The opening sections introduce block ciphers and attack models, then develop properties of balanced Feistel networks. The book gives particular attention to the H-coefficient method and the Luby–Rackoff theorems, connecting formal security results with the structures that make them possible.
These chapters offer context for understanding why round count, construction details, and the assumptions behind a proof matter when assessing a cipher.
How generic attacks expose structural limits
A substantial portion of the book studies generic attacks across classical, contracting, expanding, and generalized Feistel ciphers. Its coverage includes distinguishers and attack methods applied to different round configurations and network types. For readers studying cryptanalysis, this provides a way to compare how changes in a construction affect its analysis.
From DES to other named ciphers
The survey also turns to specific designs and families, including DES and its variants, GOST, SIMON, BEAR-LION, CAST-256, and CLEFIA. This practical strand complements the theoretical chapters by placing security analysis alongside recognizable cipher constructions.
Advanced results for deeper study
Later material addresses security proofs beyond the birthday bound, coupling techniques, mirror theory, and indistinguishability-related results. The discussion extends the book’s scope beyond introductory cryptography and into the mathematical tools used in advanced security analysis.
For cryptography students and researchers
This book is suited to readers with a grounding in cryptography and the mathematical language used to discuss security proofs and attacks. It can support deeper study of symmetric-key cryptography, Feistel constructions, and the methods researchers use to reason about block-cipher security.
User Reviews
Only logged in customers who have purchased this product may leave a review.
Original price was: $123.49.$61.74Current price is: $61.74.
There are no reviews yet.