

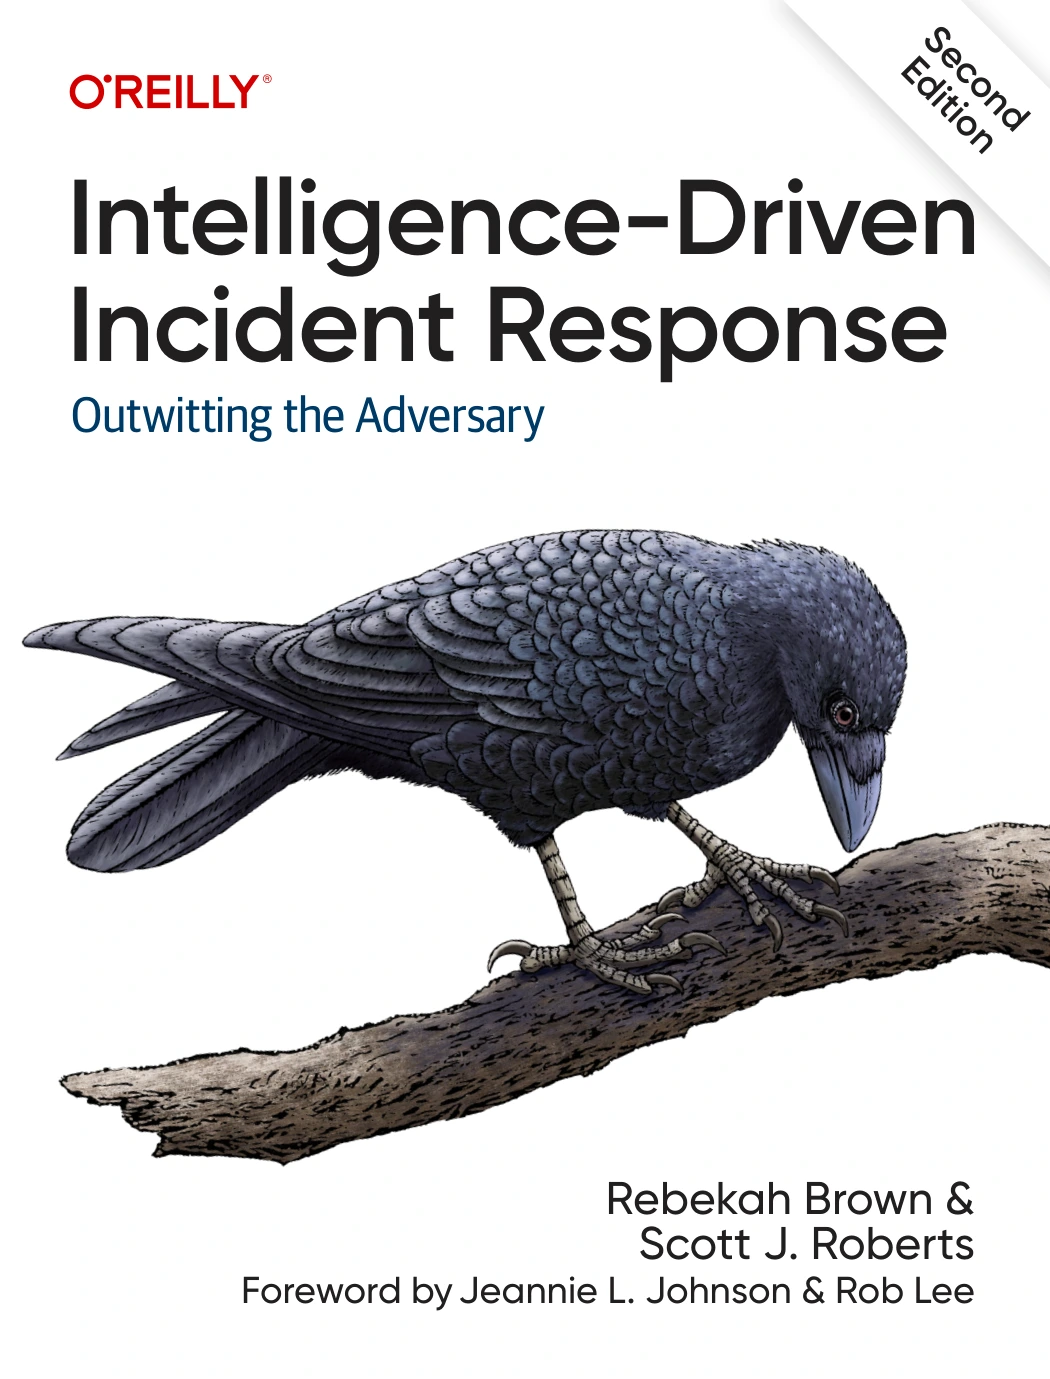
Intelligence-Driven Incident Response: Outwitting the Adversary (Second Edition)
Original price was: $56.99.$28.50Current price is: $28.50.

Rebekah Brown
Product Specs:
- File Type: PDF
- File Size: 4.0 MB
- Book Language: English
- Total Page Count: 346
- Instant Download
Incident response can do more than contain a breach. When investigators approach an intrusion with a cyber threat intelligence mindset, their findings can help explain who is acting, how they operate, and what defenders should watch for next. Intelligence-Driven Incident Response: Outwitting the Adversary shows how to connect those investigative and intelligence practices.
In this second edition, Rebekah Brown and Scott J. Roberts move from core concepts to operational application, then to the longer-term work of strategic intelligence and building an intelligence program. It is a practitioner-focused look at making incident investigations more informative—and making intelligence more useful to the teams responding to threats.
Connect intelligence with the response process
The opening section lays out the fundamentals of cyber threat intelligence and incident response, including the intelligence cycle, analytical context, confidence levels, and the relationship between data and intelligence. It also introduces response and analysis frameworks such as the Kill Chain, Diamond Model, ATT&CK, D3FEND, and F3EAD. Seeing these models alongside one another helps readers consider which lens may fit a particular investigation.
Follow the investigation from lead to action
The practical chapters apply intelligence-driven methods to targeting and intrusion work. Topics include actor-, victim-, asset-, and capability-centric targeting; network and system alerts; network, memory, and disk analysis; malware analysis; and hypothesis-led threat hunting. The book also covers what happens after an intrusion is understood: mitigation, remediation, rearchitecture, defensive actions, and the organization of incident data.
Look beyond a single incident
The final section turns to strategic intelligence and intelligence-program development. Its wider perspective considers how intelligence work can support security decisions beyond an individual investigation, and how teams can define goals, requirements, stakeholders, and measures of value.
For cybersecurity teams and analysts
This book is relevant to incident managers, cyber threat intelligence analysts, malware analysts, reverse engineers, digital forensics specialists, and security leaders looking to connect investigative work with threat intelligence. Its progression from fundamentals through practical application to program-level concerns gives readers a framework for thinking about both the incident in front of them and the defensive learning that can follow.
For teams working to understand adversary behavior—not just close an alert—this edition offers a structured way to bring intelligence and incident response into closer conversation.
User Reviews
Be the first to review “Intelligence-Driven Incident Response: Outwitting the Adversary (Second Edition)”
You must be logged in to post a review.
Original price was: $56.99.$28.50Current price is: $28.50.
There are no reviews yet.