

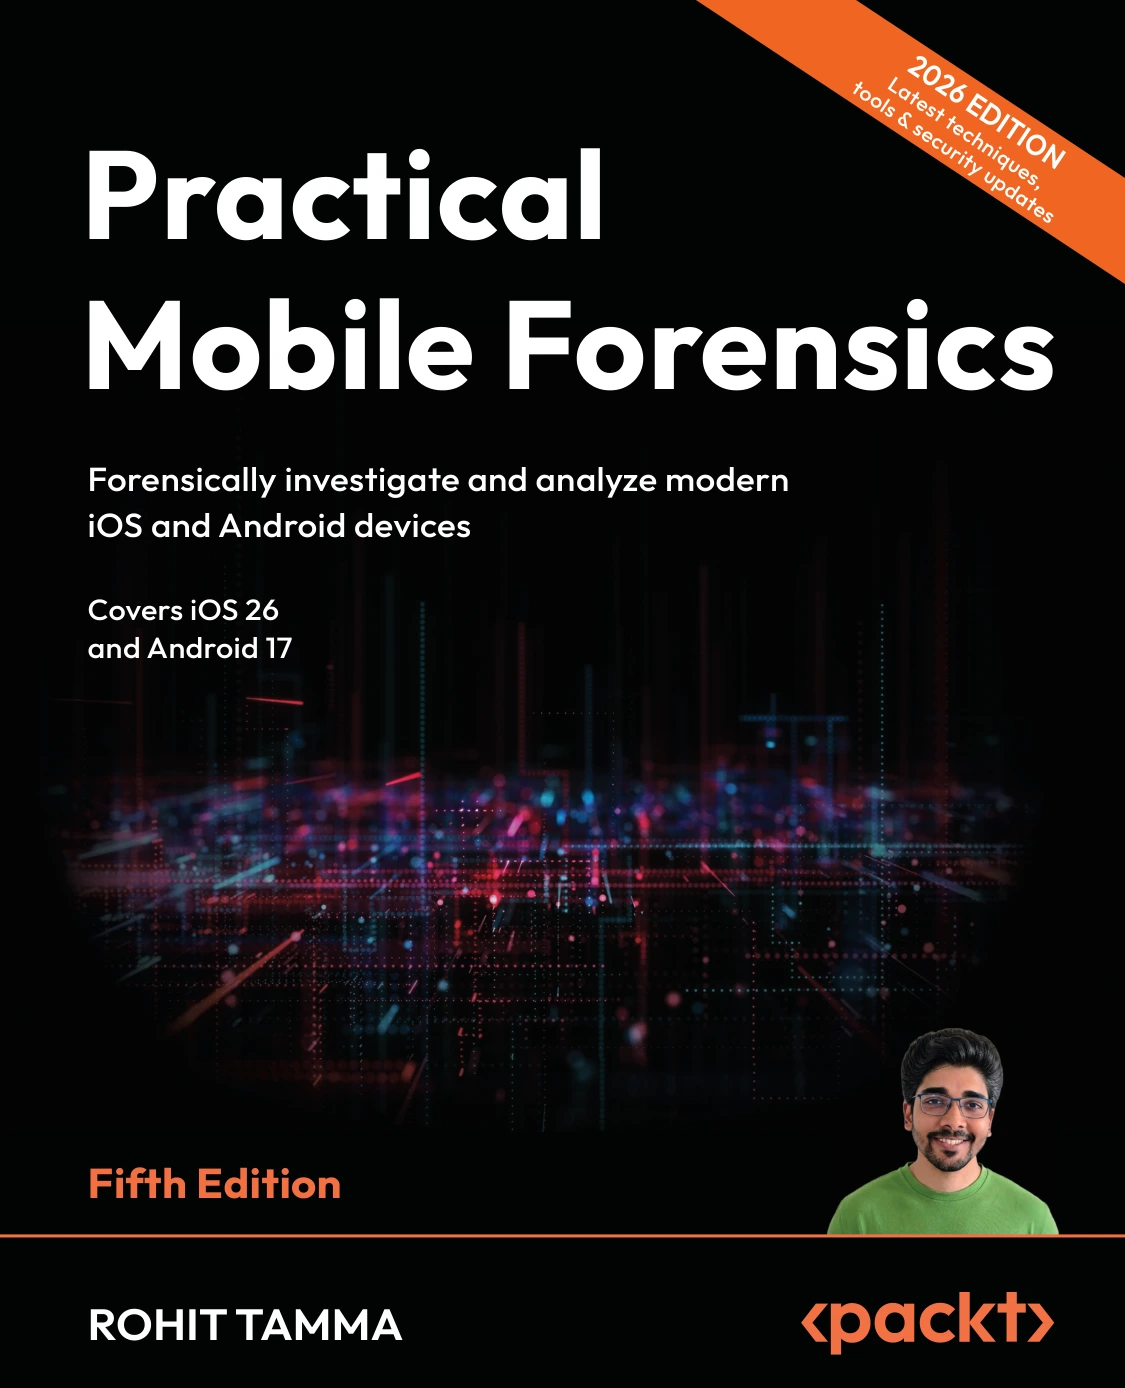
Practical Mobile Forensics, Fifth Edition
Original price was: $5.00.$2.50Current price is: $2.50.

Rohit Tamma
Product Specs:
- File Type: PDF
- File Size: 31.7 MB
- Book Language: English
- Total Page Count: 294
- Instant Download
Mobile Evidence in the Modern Device Era 🔍
Phones sit at the centre of countless investigations, and the tools used to examine them must keep pace with changing security models. Practical Mobile Forensics, Fifth Edition gives examiners a current map of the field, with iOS 26 and Android 17 in view. Written by Rohit Tamma, it moves from core forensic principles to the practical work of acquiring, verifying, and interpreting mobile data without losing sight of evidence integrity.
What the Fifth Edition Covers
The book opens with the mobile forensic investigation process: legal authority, evidence intake, isolation, acquisition, verification, analysis, documentation, and archiving. From there, it builds into platform-specific security and acquisition realities, showing why modern devices are not simply smaller computers.
A Deep Look at iOS Forensics 📱
Early chapters examine iOS architecture, filesystem changes, Secure Enclave, secure boot, app sandboxing, keychain and iCloud security, jailbreaking implications, and the extraction challenges these features create. Readers encounter normal, recovery, and DFU modes, logical and filesystem acquisition options, agent-based and jailbreak-assisted methods, unified logs, and practical walkthroughs. The backup material covers local backups, iCloud backups, encrypted versus unencrypted data, and tools such as idevicebackup2, iBackup Viewer, and Magnet AXIOM.
From Acquisition to Analysis
Later iOS material turns to interpretation: Unix, Mac absolute, and WebKit/Chrome timestamps; SQLite database structure; and core artifacts such as contacts, call history, messages, and calendar events. The emphasis is on validating tool output against raw data and understanding where artifacts come from, whether from a filesystem image or a backup.
Who This Book Is For
Digital forensics examiners, incident responders, security analysts, law enforcement investigators, and students building mobile investigation skills will find the material relevant. The walkthroughs and decision frameworks suit practitioners who need to compare acquisition paths, document their choices, and explain findings clearly.
Why This Edition Matters
Mobile forensics changes quickly. Secure Enclave protections, full-disk encryption, activation lock, remote wipe risks, and evolving OS versions all affect what an examiner can reasonably recover. This edition ties those changes to hands-on workflows, making it a useful update for readers who already know the basics and need current iOS and Android context.
User Reviews
Be the first to review “Practical Mobile Forensics, Fifth Edition”
You must be logged in to post a review.
Original price was: $5.00.$2.50Current price is: $2.50.
There are no reviews yet.