

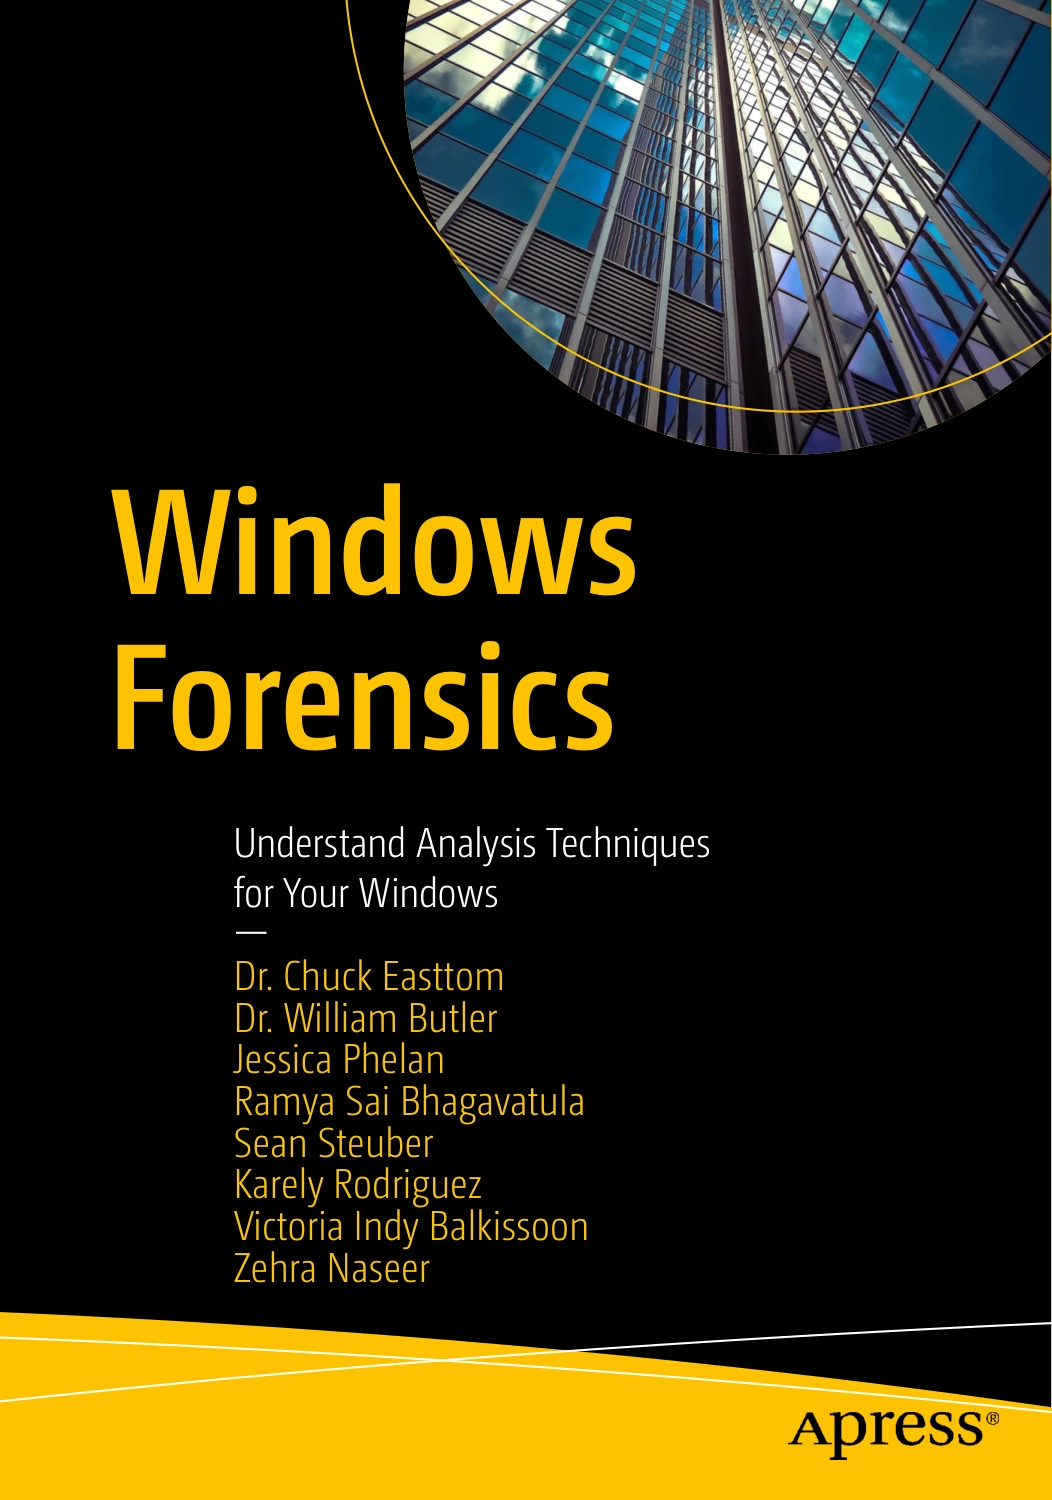
Windows Forensics: Understand Analysis Techniques for Your Windows
Original price was: $122.00.$61.00Current price is: $61.00.

Dr. Chuck Easttom
Product Specs:
- File Type: PDF
- File Size: 26.7 MB
- Book Language: English
- Total Page Count: 484
- Instant Download
Practical Windows Forensic Analysis
Windows Forensics: Understand Analysis Techniques for Your Windows takes readers inside the evidence-rich layers of Microsoft’s operating system. Rather than stopping at generic computer forensics theory, it focuses on the places where Windows leaves traces of user activity, system events, and potential intrusion.
The book builds a clear path from core concepts to hands-on techniques. Early chapters establish a foundation in Windows architecture, then move into forensic imaging, file artifacts, registry analysis, shadow copies, memory forensics, and PowerShell-based investigations.
Hands-On Tools and Techniques
Readers get practical exposure to tools such as OSForensics, FTK Imager, and Volatility Workbench. Step-by-step guidance shows how to create forensic images, mount drives, examine registry hives, and analyze memory dumps. PowerShell chapters introduce built-in commands that can support real investigative tasks.
Who This Book Is For
This ebook is a strong fit for digital forensics students, incident responders, system administrators, and anyone who needs to understand how Windows systems can be examined reliably and defensibly. The material is detailed enough for serious learners but remains approachable for those building their forensics skills.
Why the Windows Focus Matters
Because Windows is so widely deployed in corporate and government environments, the ability to interpret its artifacts is essential. This publication helps you connect raw data with meaningful forensic conclusions, whether you are preparing for an investigation, studying for certification, or expanding your technical toolkit.
User Reviews
Be the first to review “Windows Forensics: Understand Analysis Techniques for Your Windows”
You must be logged in to post a review.
Original price was: $122.00.$61.00Current price is: $61.00.
There are no reviews yet.