

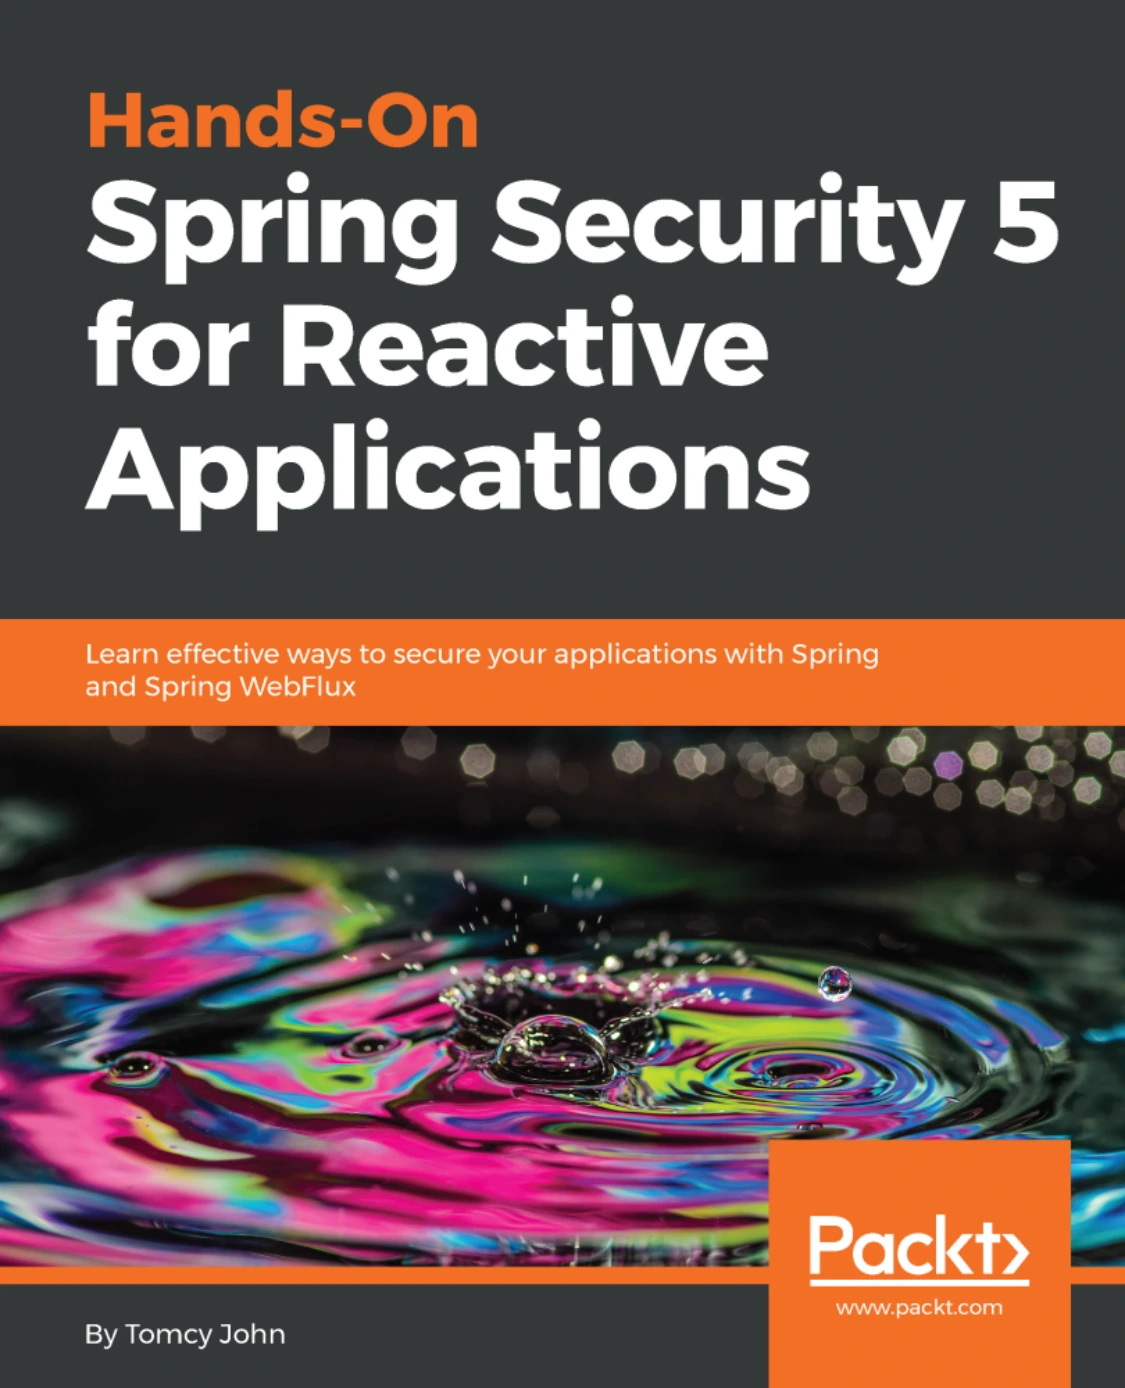
Hands-On Spring Security 5 for Reactive Applications
Original price was: $31.99.$15.99Current price is: $15.99.

Tomcy John
Product Specs:
- File Type: PDF
- File Size: 21.8 MB
- Book Language: English
- Total Page Count: 262
- Instant Download
Securing a reactive Java application calls for more than transplanting familiar rules into a new framework. Tomcy John’s Hands-On Spring Security 5 for Reactive Applications connects the foundations of Spring Security with the practical work of configuring authentication and access control across Spring MVC and Spring WebFlux projects.
Start with the security model
The opening chapters establish the vocabulary and architecture behind the examples: reactive programming, Spring’s reactive stack, authentication, authorization, and the way Spring Security processes requests. This grounding helps make later configuration decisions easier to follow, especially for developers moving between conventional web applications and reactive designs.
Work through real authentication approaches
Rather than concentrating on a single login pattern, the book explores several ways applications can verify identity. Topics include SAML, LDAP, OAuth 2.0 and OpenID Connect, as well as CAS and JAAS. Along the way, readers encounter practical setup and configuration work, making the material useful when comparing approaches for a particular Spring application.
Bring security into WebFlux and APIs
Spring WebFlux receives dedicated attention, including its relationship to Spring MVC and the reactive security architecture. Further coverage addresses REST API security and authorization, helping readers consider how access controls apply across web endpoints and application services.
Explore the wider application landscape
The book also looks at securing microservices and serverless applications, along with add-ons such as HDIV, the Crypto Module, and CORS support. These subjects broaden the discussion beyond a basic login flow to the surrounding components and deployment patterns developers may need to account for.
Built around focused examples
Examples use small projects to explain individual concepts, with Spring Boot, Maven, Java configuration, and occasional XML configuration among the approaches covered. The structure is suited to readers who want to study a particular security mechanism and then see how it fits into a working Spring-based application.
Who will find it useful?
This technical guide is aimed at Java developers who already have some familiarity with Spring and Spring Security and want to understand their reactive applications more deeply. It can also serve as a topic-based reference for developers reviewing authentication options, WebFlux security, or Spring Security 5 integrations.
User Reviews
Only logged in customers who have purchased this product may leave a review.
Original price was: $31.99.$15.99Current price is: $15.99.
There are no reviews yet.