

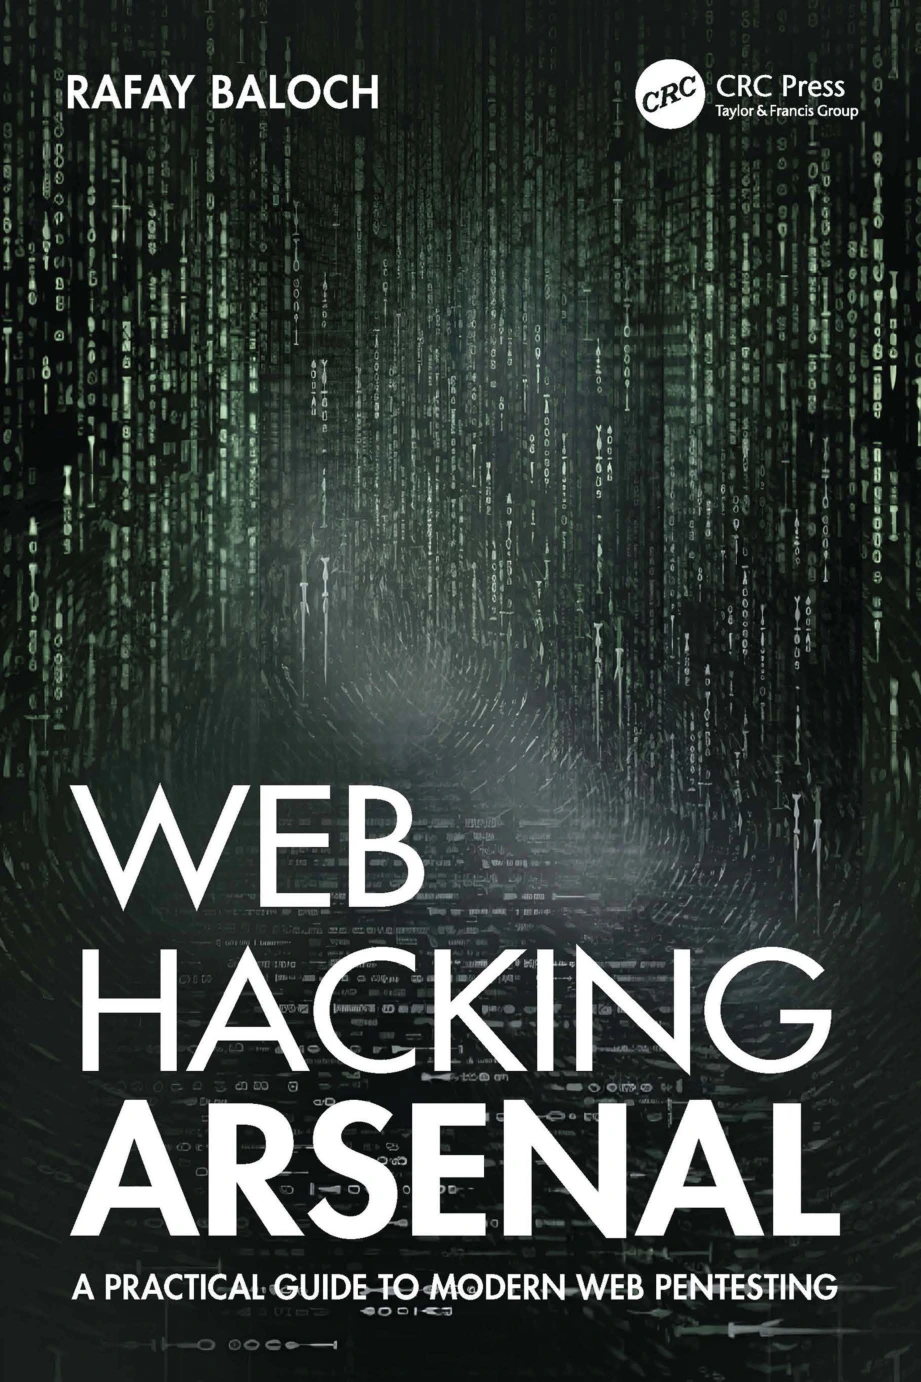
Web Hacking Arsenal: A Practical Guide to Modern Web Pentesting
Original price was: $5.00.$2.50Current price is: $2.50.

Rafay Baloch
Product Specs:
- File Type: PDF
- File Size: 48.6 MB
- Book Language: English
- Total Page Count: 578
- Instant Download
Understanding the Modern Web Attack Surface 💻
Rafay Baloch’s Web Hacking Arsenal: A Practical Guide to Modern Web Pentesting tackles the realities of testing web applications in a landscape that changes daily. Rather than relying on sanitized lab exercises, this book draws from real-world scenarios and field experience, giving readers a practical framework for identifying and exploiting vulnerabilities across modern web technologies.
Key Coverage and Practical Depth
- HTTP fundamentals, browser internals, and core security policies
- Intelligence gathering, subdomain enumeration, and cloud misconfiguration hunting
- Server-side injection attacks: SQLi, RCE, SSTI, and NoSQL exploitation
- Client-side attacks: XSS, DOM clobbering, CSP bypass, and mutation XSS
- Real-world case studies and bug bounty strategies
What Makes This Guide Stand Out
Baloch blends theoretical understanding with actionable technique, moving beyond tool-centric tutorials to explain the reasoning behind each attack. The content emphasizes adaptability, preparing readers to respond to threats that haven’t yet emerged. Coverage of up-to-date vulnerability testing methods and browser security internals distinguishes this from many traditional manuals.
Who Should Read This Book
Security professionals, penetration testers, bug bounty hunters, and developers who want to understand how web applications are attacked will find a deep, structured resource here. Because the material builds from core concepts to advanced exploitation, it supports both newer practitioners and those looking to sharpen their offensive security skills.
With a focus on real-world challenges, Web Hacking Arsenal is a forward-looking reference for anyone serious about modern web application security.
User Reviews
Be the first to review “Web Hacking Arsenal: A Practical Guide to Modern Web Pentesting”
You must be logged in to post a review.
Original price was: $5.00.$2.50Current price is: $2.50.
There are no reviews yet.