

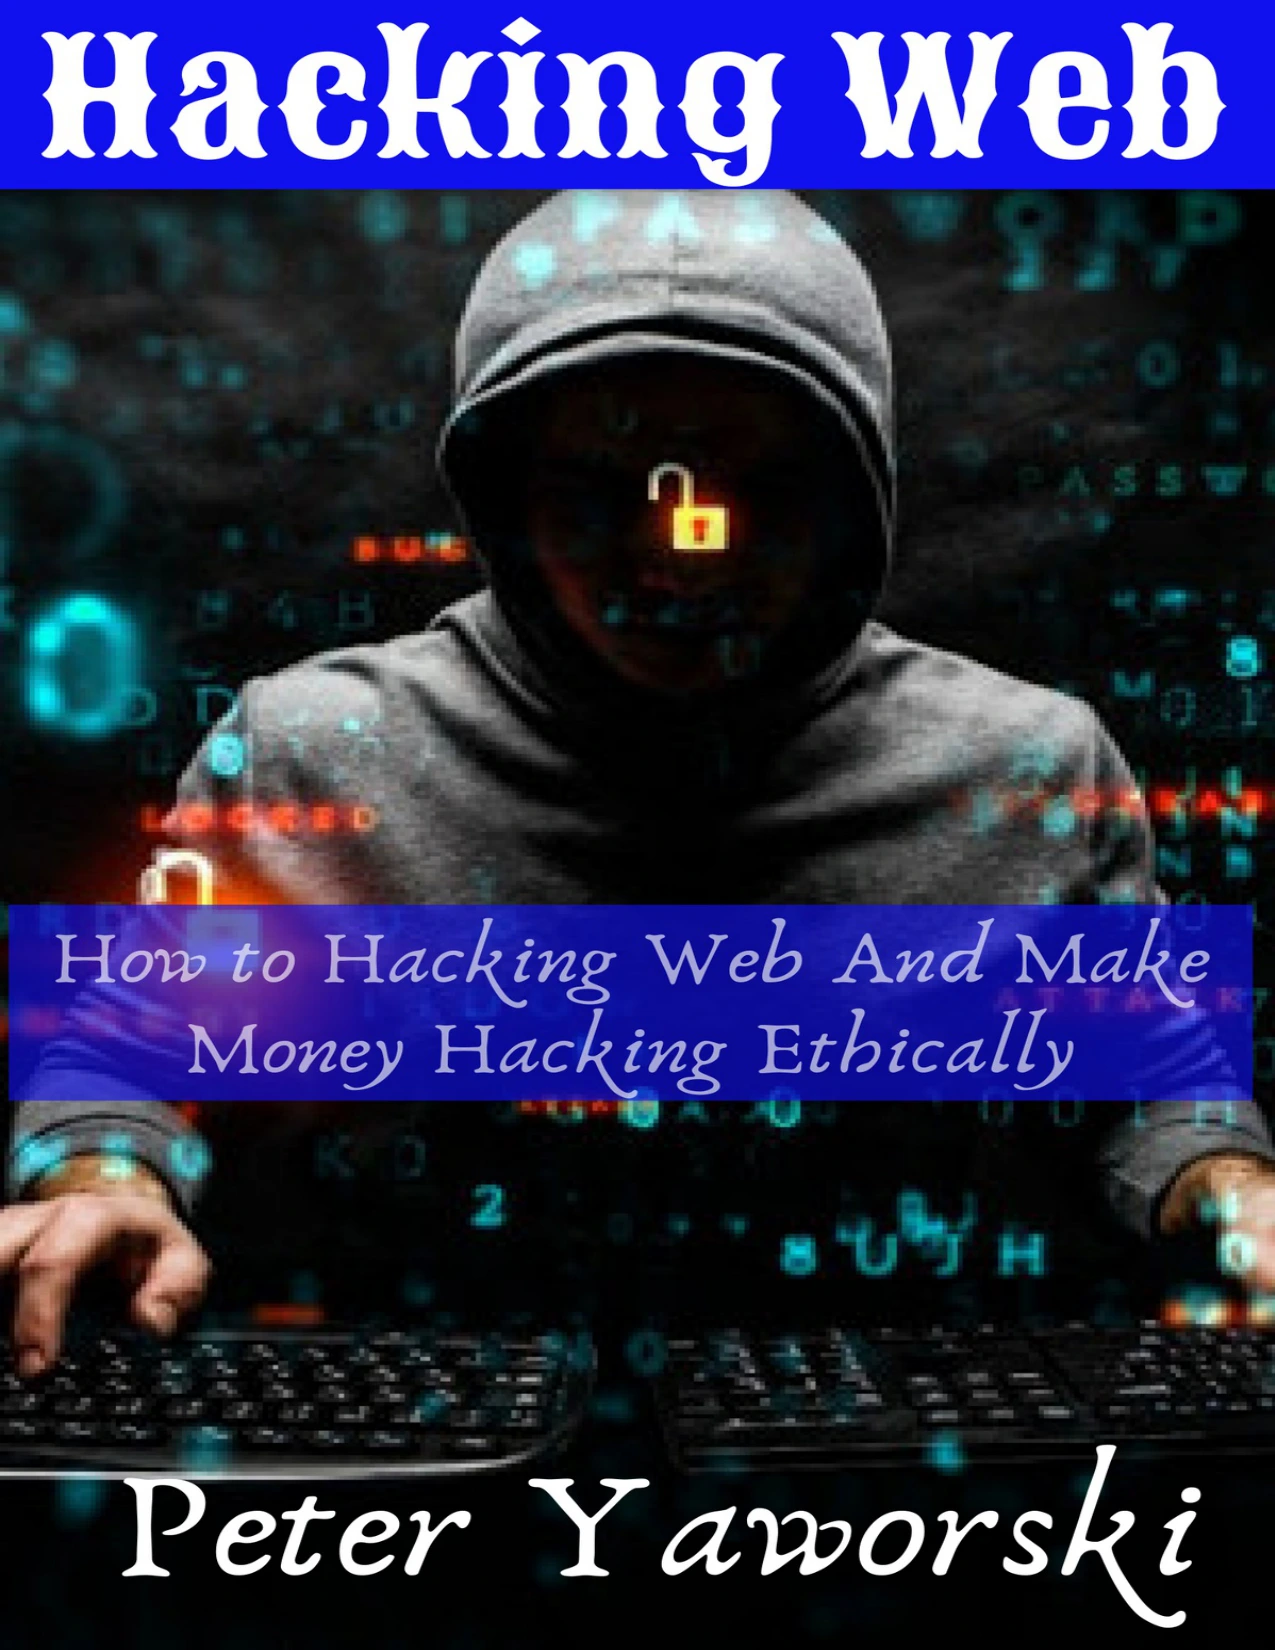
Hacking Web: How to Hacking Web And Make Money Hacking Ethically
Original price was: $5.00.$2.50Current price is: $2.50.

Peter Yaworski
Product Specs:
- File Type: PDF
- File Size: 2.9 MB
- Book Language: English
- Total Page Count: 181
- Instant Download
Real vulnerability reports can make web security easier to understand than abstract warnings alone. Peter Yaworski’s book uses disclosed cases to examine how weaknesses in websites and applications arise, how researchers investigate them, and how findings are reported in an ethical context.
The examples span familiar web-security problems—from cross-site scripting and SQL injection to application logic flaws and server-side request forgery—alongside cases involving companies such as Shopify, Twitter, Google, and Uber. The emphasis is on learning from reported incidents, not treating hacking as a bag of tricks.
Learn from vulnerabilities found in the wild
The book works through a wide range of vulnerability classes, including HTML and HTTP parameter issues, CRLF injection, cross-site request forgery, open redirects, subdomain takeover, XML external entity vulnerabilities, remote code execution, and memory-related bugs. Seeing different kinds of flaws side by side helps readers recognize how varied web application security problems can be.
From investigation to responsible reporting
Its scope extends beyond individual vulnerabilities. Later sections address information gathering, application testing, digging deeper into potential findings, and writing vulnerability reports. That combination makes the publication relevant to readers interested not only in identifying security issues, but also in explaining them clearly and responsibly.
Tools and practical context
Named tools such as Burp Suite and Knockpy appear alongside the case-based material. The examples and tool references give readers concrete context for exploring web security concepts, while the range of reported incidents shows why careful testing and clear communication matter.
For readers exploring ethical web security
This book may interest aspiring bug bounty hunters, web developers building their security knowledge, and readers curious about how publicly disclosed vulnerabilities are analyzed. Its central thread is practical: understand the weakness, study how it appeared, and treat responsible disclosure as part of the work.
User Reviews
Be the first to review “Hacking Web: How to Hacking Web And Make Money Hacking Ethically”
You must be logged in to post a review.
Original price was: $5.00.$2.50Current price is: $2.50.
There are no reviews yet.