

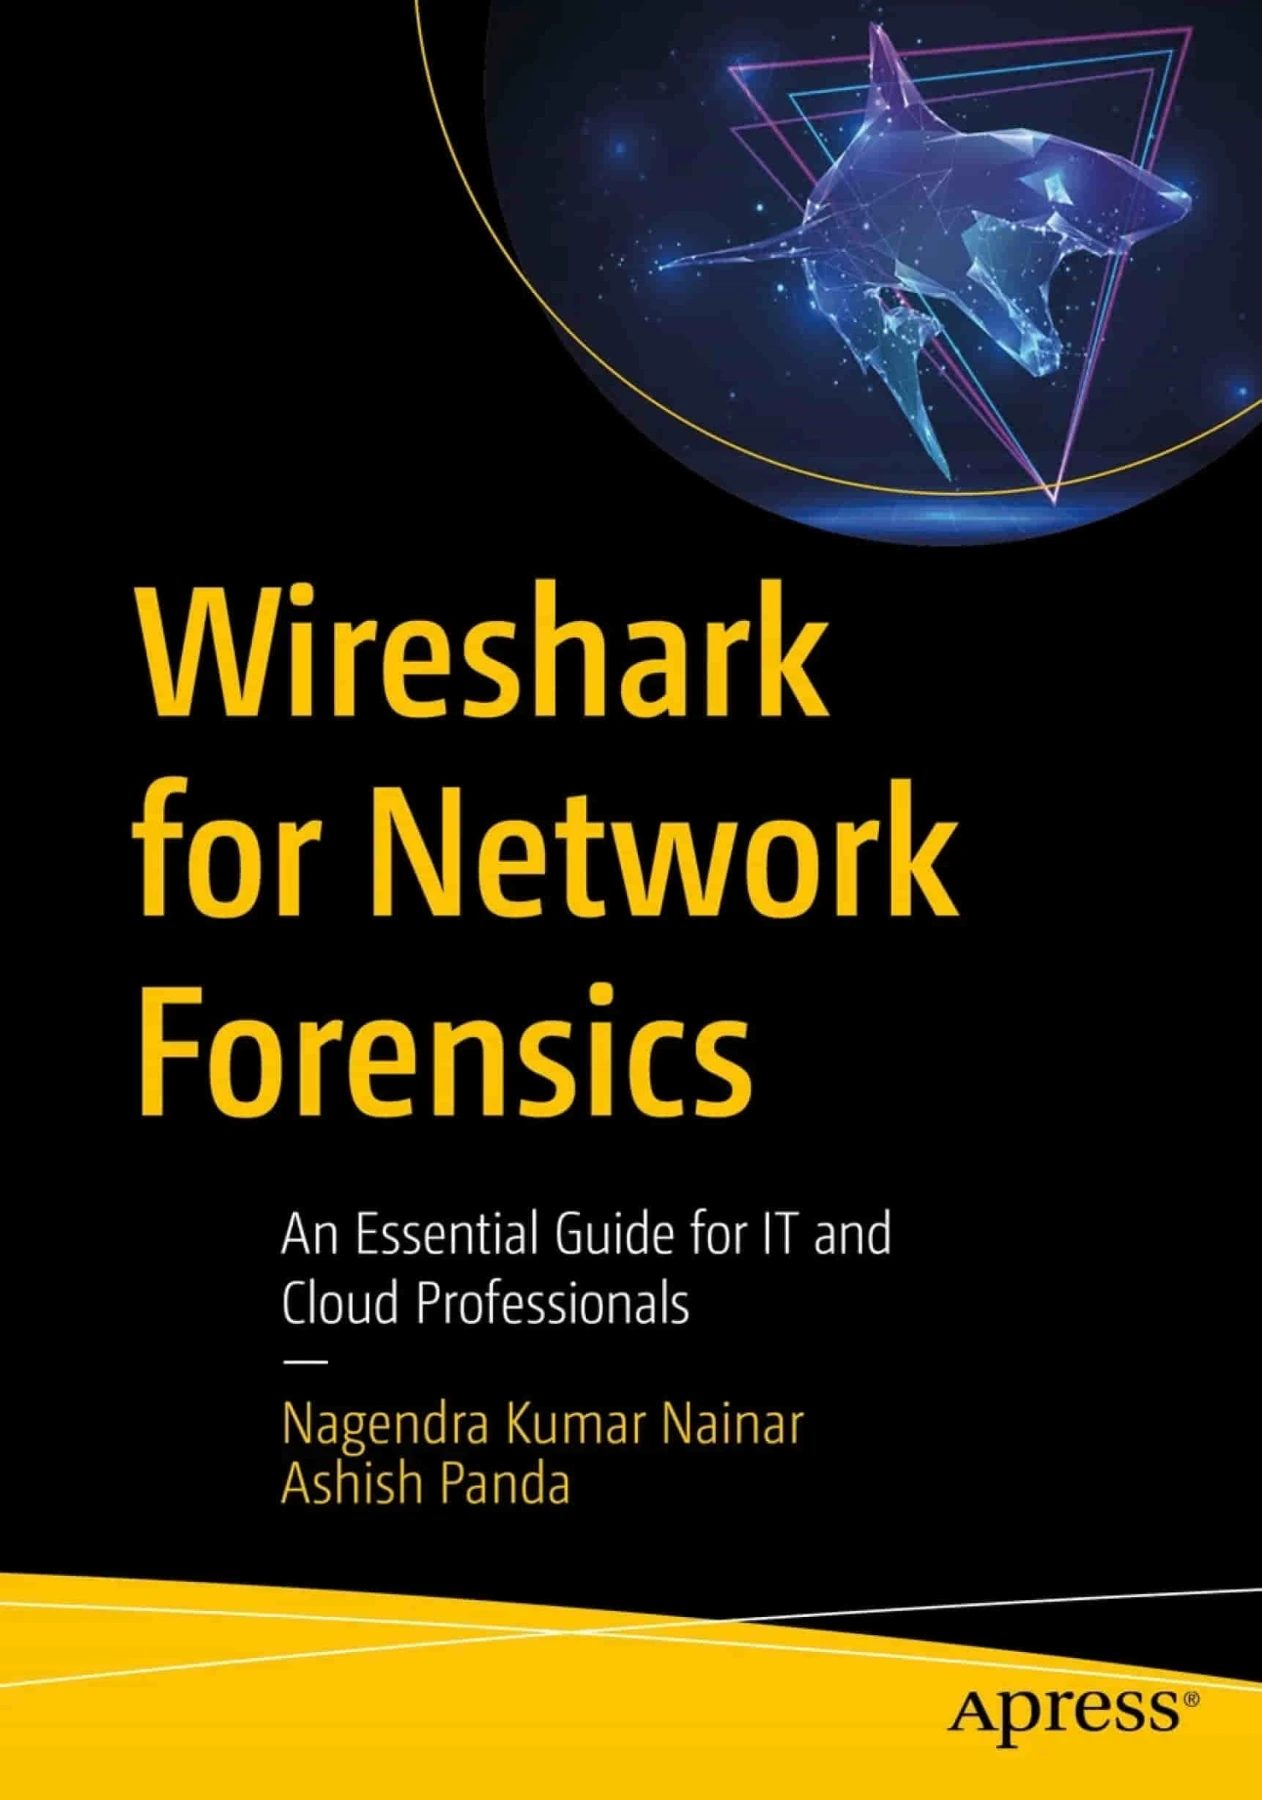
Wireshark for Network Forensics: An Essential Guide for IT and Cloud Professionals
Original price was: $5.00.$2.50Current price is: $2.50.

Nagendra Kumar Nainar
Product Specs:
- File Type: PDF
- File Size: 24.5 MB
- Book Language: English
- Total Page Count: 283
- Instant Download
Network traffic tells a story—if you know how to listen. Wireshark for Network Forensics: An Essential Guide for IT and Cloud Professionals is built for practitioners who need to turn raw packets into actionable evidence, whether they’re troubleshooting cloud connectivity, investigating a security incident, or validating application behavior.
A Practical Path Through the Packet Landscape
Authors Nagendra Kumar Nainar and Ashish Panda open with the core Wireshark skills you’ll rely on every day: stream graphs, flow visualization, and following packet streams. From there, the book moves through systematic capture planning, advanced filtering, and remote packet collection.
Secured Traffic Without the Blind Spots
Modern encryption doesn’t have to end your analysis. The book explains how to handle HTTPS, QUIC, and secure DNS traffic, including practical decryption workflows for TLS-based protocols. It’s a clear-eyed look at what you can—and cannot—inspect when applications protect their data in transit.
Wireless, Multimedia, and Cloud-Native Capture
- Wireless LAN capture: 802.11 frame types, endpoint onboarding, and WLAN statistics.
- Multimedia analysis: HTTP file extraction, RTP video, SIP over TLS, and telephony troubleshooting.
- Cloud and containers: Capturing traffic in AWS, GCP, Docker, and Kubernetes environments.
Forensics, Malware, and Custom Dissectors
The forensic chapters explore packet spoofing, scanning, denial-of-service attacks, and malware analysis workflows. You’ll also learn how to create custom Wireshark dissectors using the Wireshark Generic Dissector (WSGD), which is invaluable when proprietary protocols need decoding.
Who This Book Serves
This guide is aimed squarely at IT and cloud professionals, network engineers, security analysts, and forensic investigators. It assumes a working understanding of networking fundamentals but does not demand prior Wireshark expertise. The practical orientation means you’ll spend less time reading about menu options and more time applying capture strategies to real traffic.
Wherever your packets travel—across a campus Wi-Fi, through a container mesh, or into a public cloud—this book gives you the disciplined framework to follow them with confidence.
User Reviews
Be the first to review “Wireshark for Network Forensics: An Essential Guide for IT and Cloud Professionals”
You must be logged in to post a review.
Original price was: $5.00.$2.50Current price is: $2.50.
There are no reviews yet.